
Secure Enterprise Messaging Platform
Zeour NOVARYX is a secure enterprise messaging platform for official internal communications. It combines encrypted conversations with organisation-controlled directories, archives and administration. Editions are scoped to the organisation, including branding, deployment and field communication requirements.
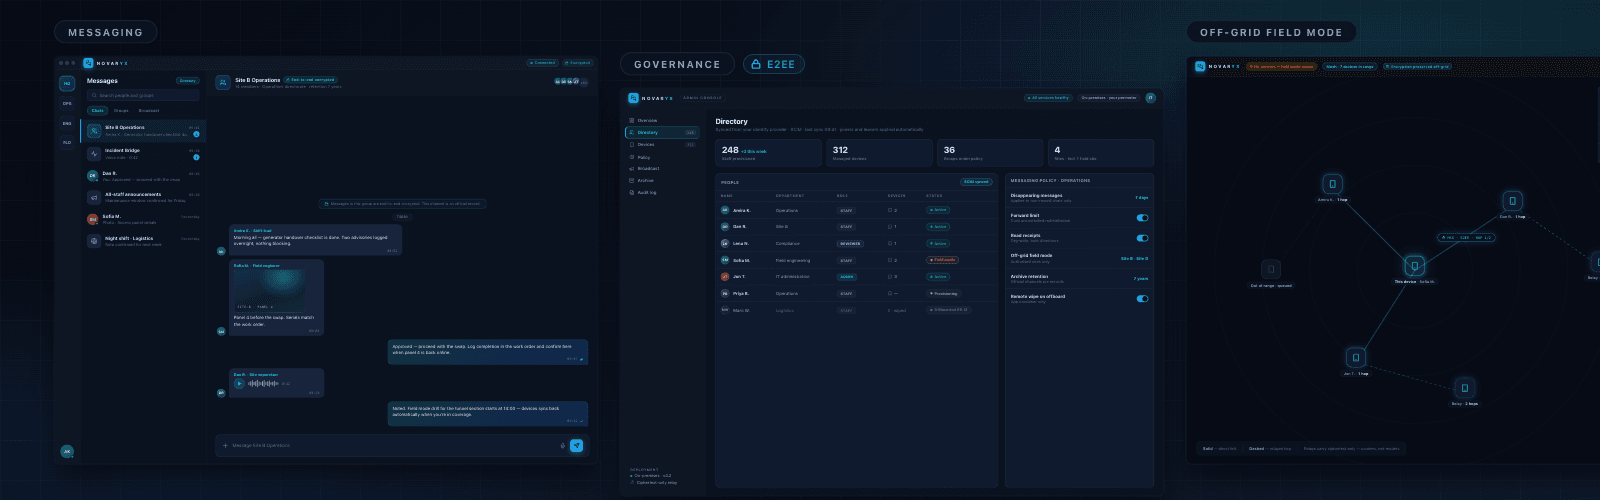
Governed Internal Messaging for Organisations
Provide an official communication channel with user and device lifecycle controls. NOVARYX brings messaging, calls, administration and archive governance into a scoped edition, with off-grid field mode described in the platform modules below.
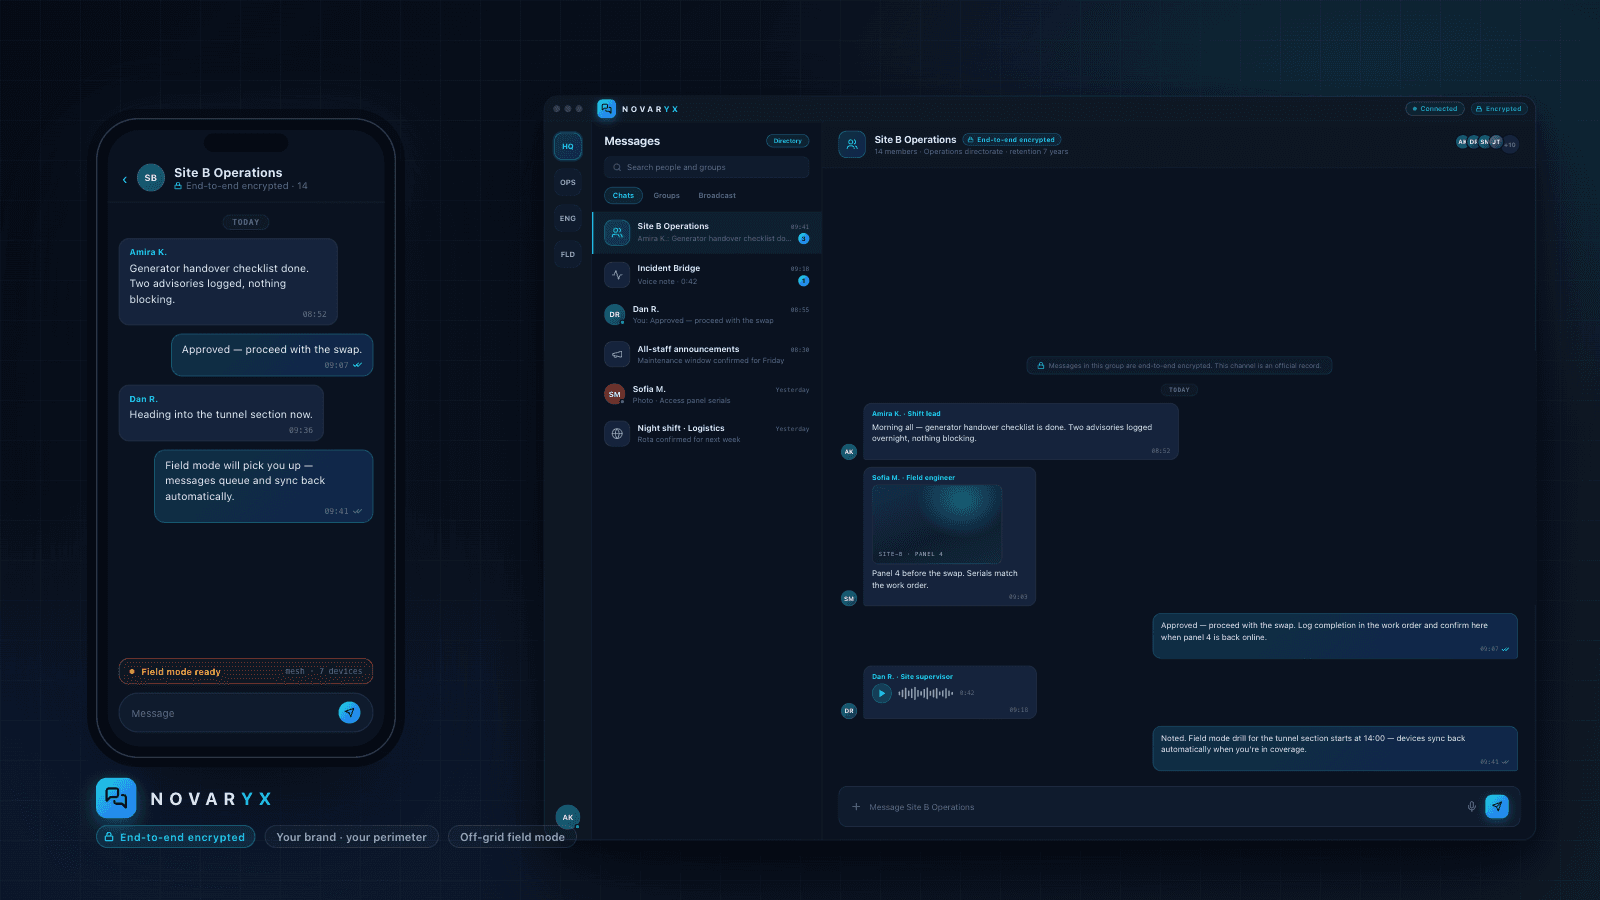
Scoping the Communication Platform
Use enterprise software development for custom workflow and system integration requirements. Digital transformation consulting can help assess the operational and deployment brief.
For the physical side of organisational access, explore the separate visitor management system. It addresses facility arrivals and reception records.
Encrypted Messaging, Directory Controls and Archive Governance
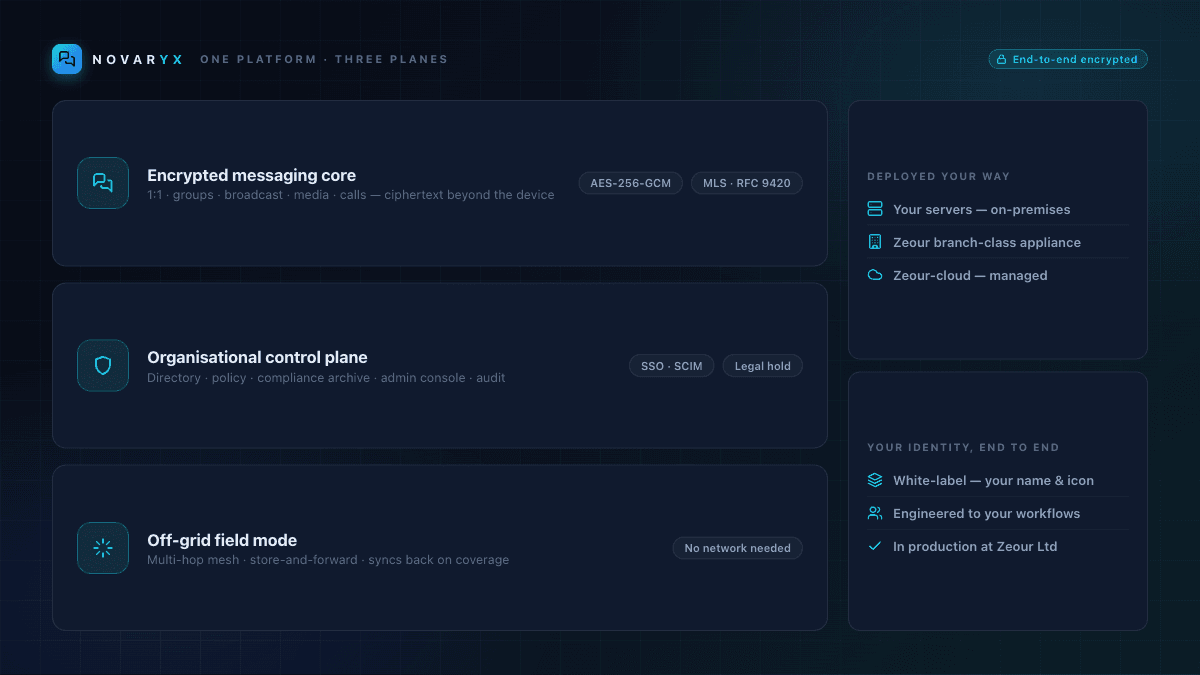
NOVARYX is a secure communications platform, not a seat subscription: an end-to-end encrypted messaging core, an organisational control plane (directory, policy, archive, administration), and an off-grid field mode — assembled into a branded edition engineered to each customer's workflows, platforms, and regulatory obligations. The backend runs inside your perimeter (or on Zeour-cloud where preferred), stores ciphertext only, and is governed entirely by your organisation. Engineered multilingual — full RTL as a production baseline, any locale per engagement. The reference implementation carries Zeour Ltd's own official communications in daily production.
Zeour NOVARYX — a white-label, end-to-end encrypted messaging platform for official internal communications. Engineered per engagement to each organisation's exact workflows: sovereign on-premises or Zeour-cloud deployment, org-directory access control, compliant message archiving held by your organisation, encrypted media and calls, and an off-grid field mode that keeps teams messaging over multi-hop mesh when there is no network. In production at Zeour Ltd for our own official communications. Editions are scoped to the organisation — a 30-person firm on Zeour-cloud is as valid a deployment as a 5,000-seat sovereign estate.
Key Functionalities
Encrypted Messaging Core
End-to-end encrypted 1:1 and group messaging built on open, audited cryptographic standards — AES-256-GCM content encryption, modern key agreement with a post-quantum-ready design, MLS-aligned (RFC 9420) group encryption, and per-sender message signing so a group member cannot impersonate another.
The security heart of the platform — content encrypted on the sender's device, decrypted on the recipient's, ciphertext everywhere between.
- AES-256-GCM authenticated content encryption
- Post-quantum-ready key agreement design
- MLS-aligned (RFC 9420) group encryption
- Per-sender message signing inside groups
- Identity-key pinning with security-change alerts
Groups, Channels & Broadcast
Directory-governed groups (department, site, shift, project), open rooms where policy allows, and one-to-many broadcast channels with read tracking for announcements — each with role-based membership and admin controls.
Encrypted Media & Voice Notes
Images, documents, and voice notes sealed with per-message content keys; ciphertext blobs stored on your infrastructure; metadata stripped from shared media on-device before it ever leaves the sender.
Encrypted Voice & Video Calls
Standards-based WebRTC calling with encrypted signalling over the messaging envelope and self-hosted relay infrastructure inside your perimeter — no third-party calling service in the path.
Message Lifecycle Controls
Edit and delete-for-everyone windows, disappearing messages with policy-set timers, view-once media, starred messages, reply threading, and forward limits that curb uncontrolled redistribution — each configurable per deployment policy.
Encrypted On-Device Storage & Search
The local message store and its search index are encrypted at rest on every device; search runs entirely on-device so plaintext never reaches a server; deletion and disappearing-message purges zeroize the index.
Private Notifications
Push payloads carry ciphertext only; the device decrypts locally to show a preview, and degrades to a generic notification for protected content — message content never transits notification infrastructure in plaintext.
Off-Grid Field Mode
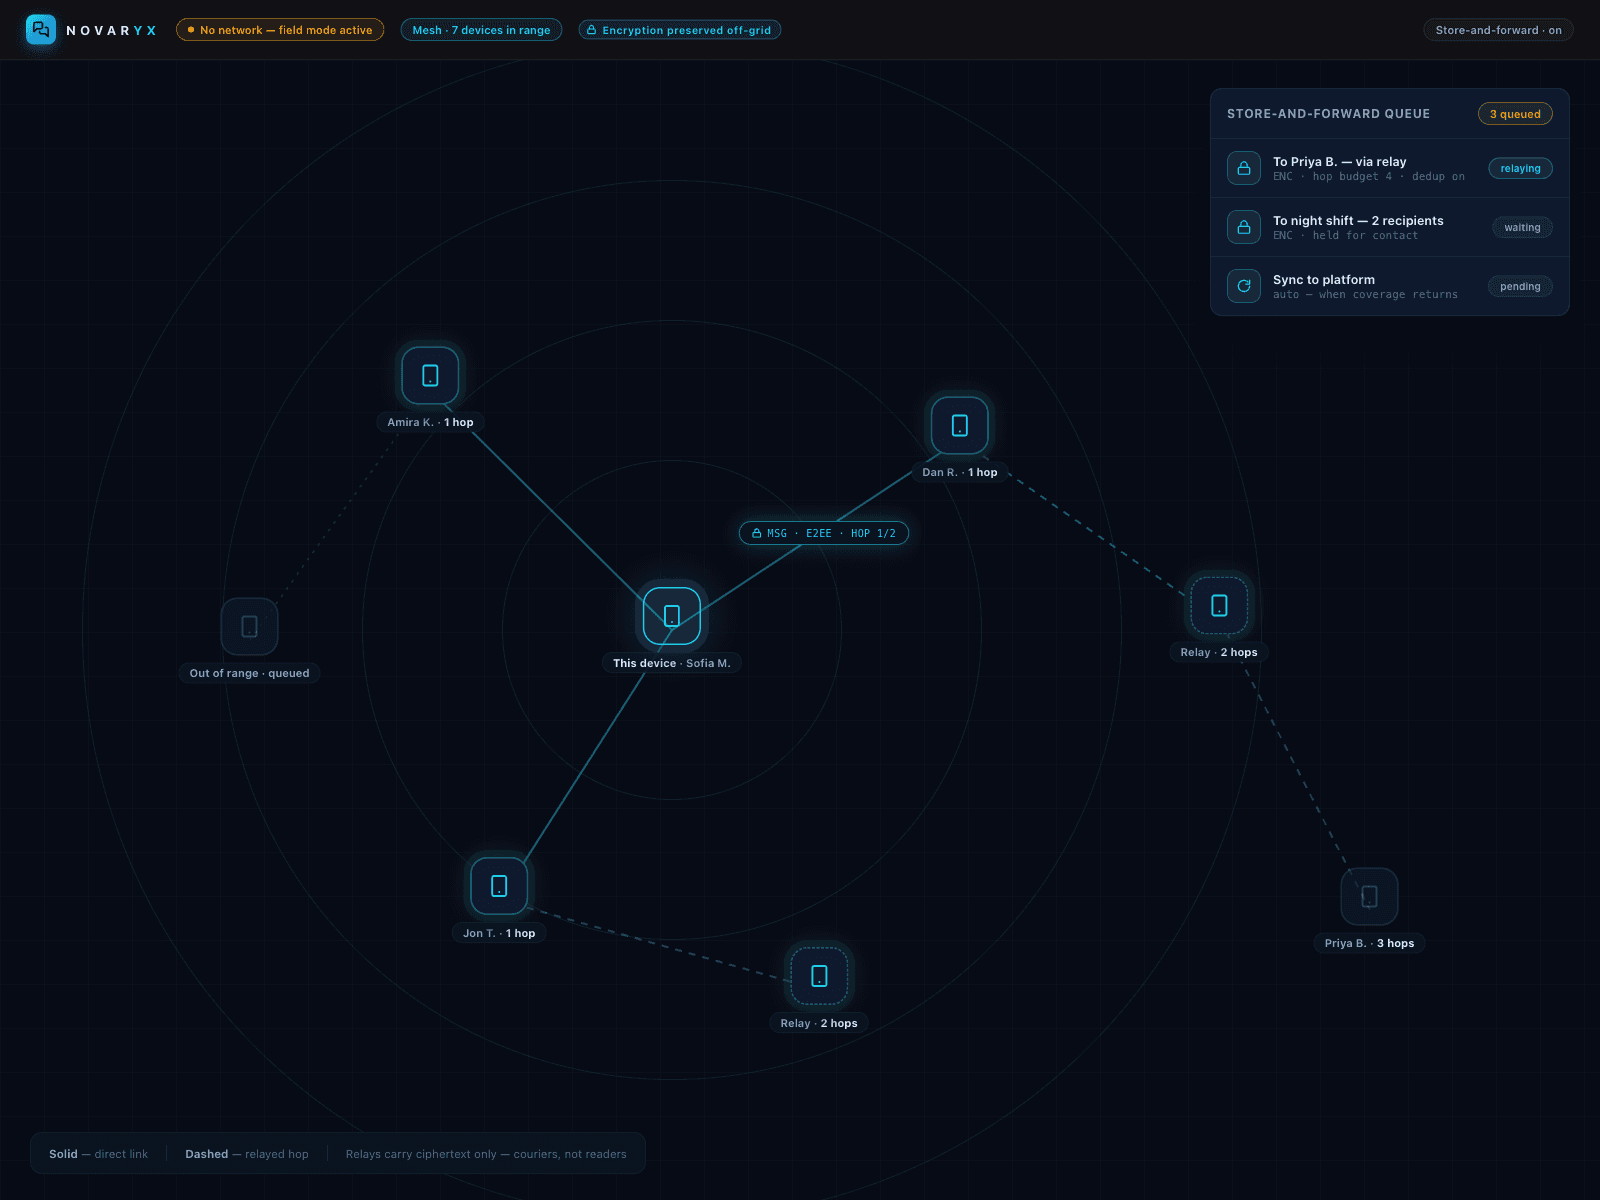
Multi-hop mesh messaging over short-range radio with store-and-forward relay, hop budgets, and deduplication — encrypted messages hop device-to-device where there is no network, then reconcile with the platform when connectivity returns.
Communication that survives the absence of infrastructure.
- Multi-hop mesh over short-range radio
- Store-and-forward with hop budgets and deduplication
- End-to-end encryption preserved off-grid
- Automatic reconciliation on reconnect
- Site survey and radio trials per deployment
Org Directory & Policy Engine
Who can message whom, who can create groups, which features are enabled for which roles, receipt and presence behaviour, retention windows — expressed as organisational policy against the directory, not left to individual users.
Organisational reality as the access model — people, departments, sites, roles, and the rules that bind them.
- Directory-scoped messaging permissions
- Role- and site-based feature policy
- Group and broadcast governance
- Receipt, presence, and retention policy per deployment
- Field-mode authorisation control
Compliance Archive & Legal Hold
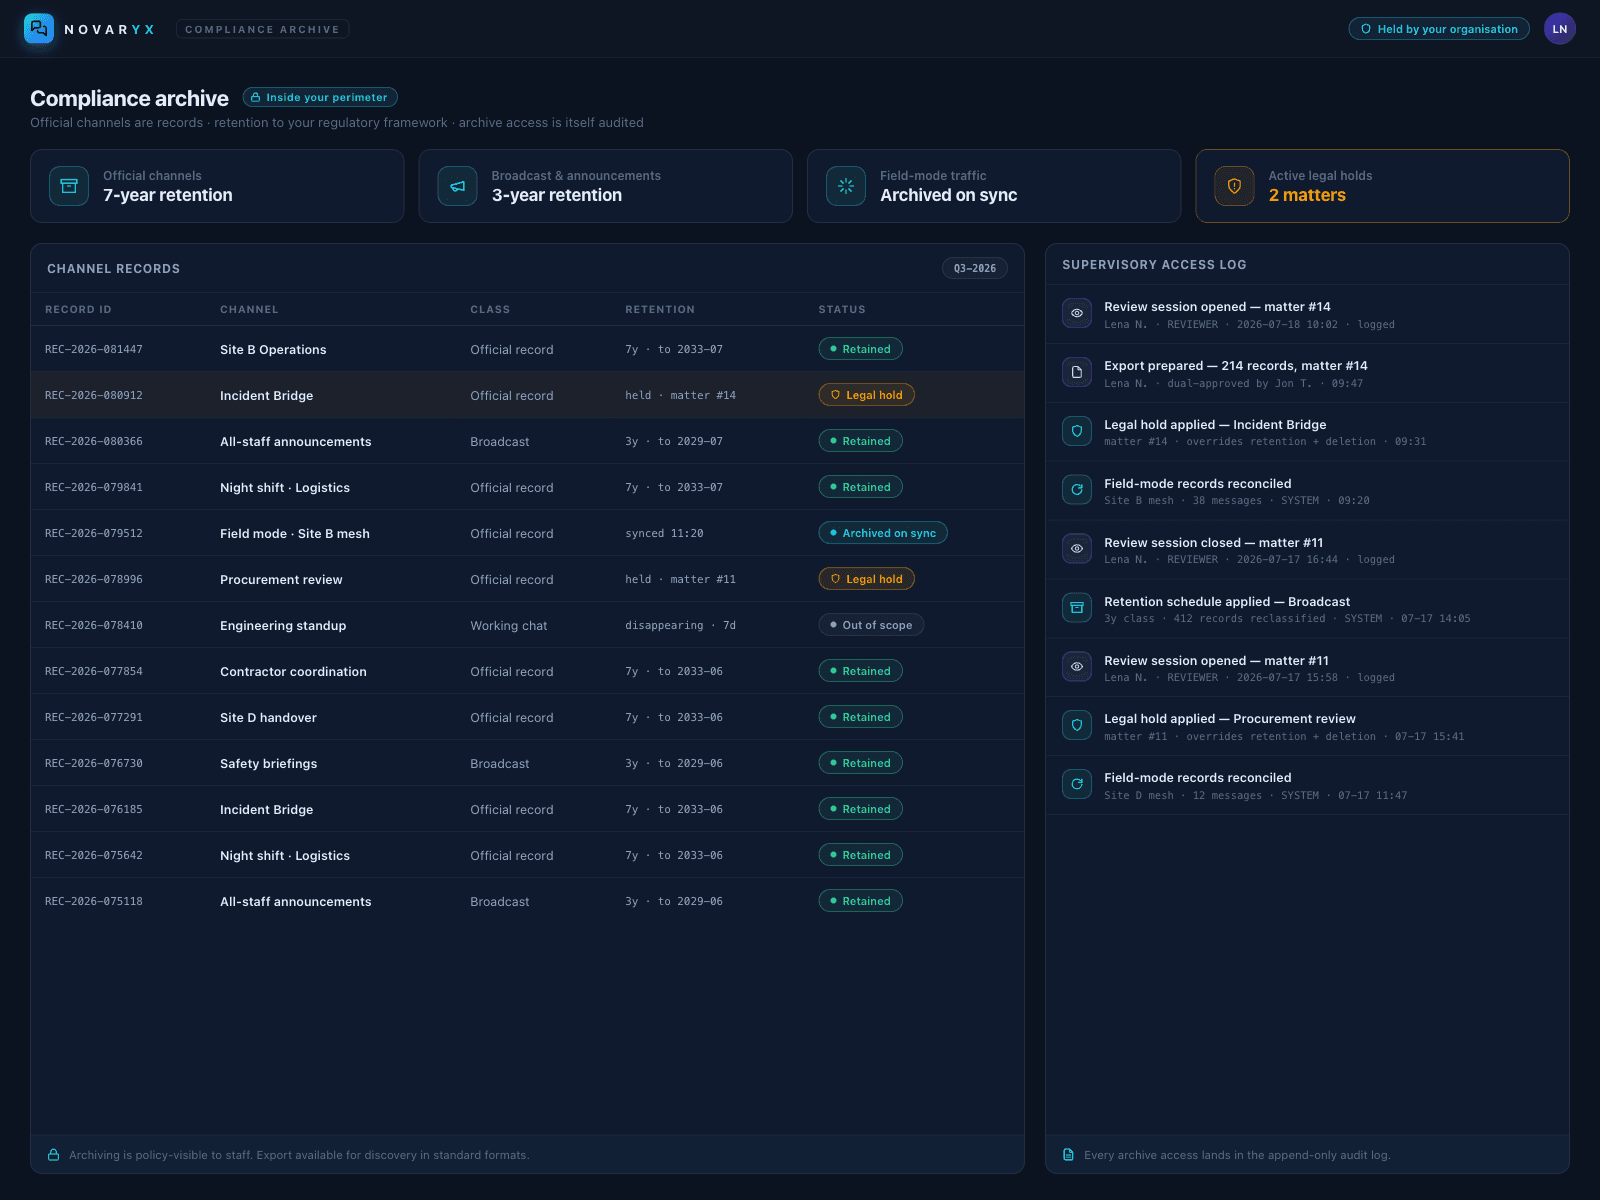
An organisation-held archive engineered to your regulatory framework: retention schedules, supervisory review, legal hold, export for discovery, and a complete audit trail of archive access itself.
Records obligations met without abandoning encryption — an archive your organisation holds and governs.
- Retention schedules to your regulatory framework
- Supervisory review with audited access
- Legal hold and discovery export
- Policy-visible archiving staff can trust
- GDPR / PDPL-aligned data-subject workflows
Admin Console
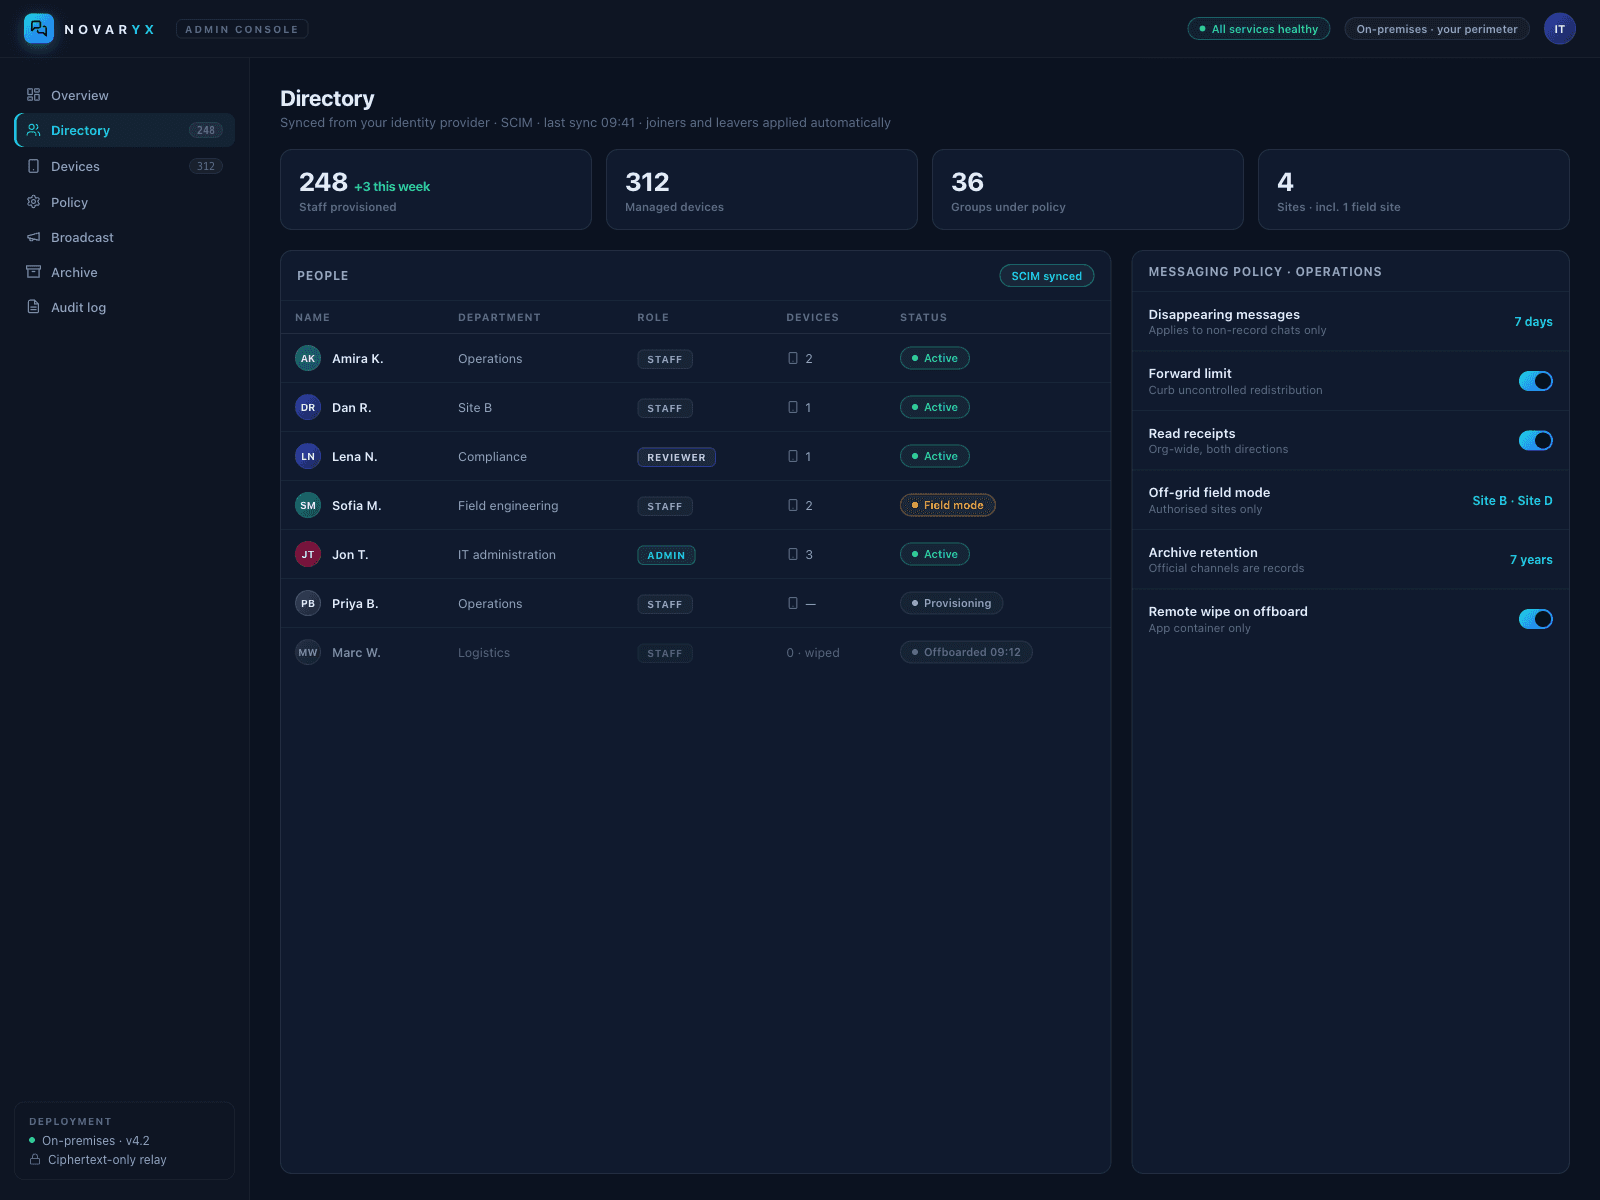
User and device lifecycle, policy management, remote wipe of the app container, usage and adoption reporting, broadcast administration, and an append-only audit log of every administrative action.
Identity & Provisioning
SAML 2.0 / OIDC single sign-on against your identity provider; SCIM keeps the directory synchronised with HR reality — joiners, movers, and leavers handled automatically, sessions revoked on offboarding.
White-Label & Multi-Platform
Your name, icon, colours, and store or MDM listing across the platform matrix scoped for your workforce — mobile, tablet, desktop, and web per engagement, distributed through your device-management tooling.
Engineered Multilingual
Full right-to-left support as a production baseline with locale-aware formatting throughout; additional locales are configuration-level additions per engagement, not re-engineering.
Software Components
Client Applications
Branded Mobile Apps
Your organisation's messenger for phones and tablets — encrypted local store, on-device search, private notifications, MDM-distributed under your identity.
Desktop & Web Clients
Per-engagement desktop and browser clients for office-based staff, sharing the same encrypted session model and organisational policy as mobile.
Field-Mode Module
The off-grid radio and relay layer inside the client — mesh discovery, store-and-forward queueing, and automatic reconciliation when the network returns.
Messaging Backend (Your Perimeter)
Delivery Service
Relays and queues ciphertext envelopes with durable store-and-forward semantics, backlog replay on reconnect, and consume-after-delivery cleanup so the server holds no more than it must.
Encrypted Media Store
Holds sealed media blobs only — content keys travel inside the encrypted message envelope, never stored server-side.
PostgreSQL-Based Data Layer
A proven relational core for directory, policy, queue, and archive state — operable, backupable, and auditable by your own DBA team.
Enterprise Control Plane
Org Directory Service
The authoritative model of people, departments, sites, roles, and devices — the object every messaging and archive policy binds to.
Policy Engine
Evaluates messaging permissions, feature availability, retention rules, and field-mode authorisation per user, group, and context.
Compliance Archive
Organisation-governed retention, supervisory review, legal hold, and export — engineered to the regulatory framework mapped in discovery.
Admin Console & Audit Log
The operational surface for IT and compliance teams, with every administrative action recorded append-only.
Identity & Integration
SSO Bridge (SAML 2.0 / OIDC)
Authentication delegated to your identity provider; no parallel password estate.
SCIM Provisioning Endpoint
Directory lifecycle synchronised from your HR / IdP source of truth.
REST API + Webhooks
Broadcast publishing, directory operations, archive export, and event forwarding for integration with ERP, CRM, ITSM, and SIEM platforms.
Hardware Components
On-Premises Deployment Options
Branch-Class Server Appliance
The messaging backend pre-installed and hardened on Zeour's industrial branch-class server hardware — one vendor for software, hardware, deployment, and AMC. See the hardware catalogue on the queue-management page.
Managed Device Fleet Provisioning
Corporate device fleets prepared for field deployments — MDM enrolment, app distribution, and radio configuration for sites that run off-grid field mode.
Self-Hosted Call Relay Node
Media relay infrastructure for encrypted voice and video calling deployed inside your perimeter, sized to concurrent-call requirements during discovery.
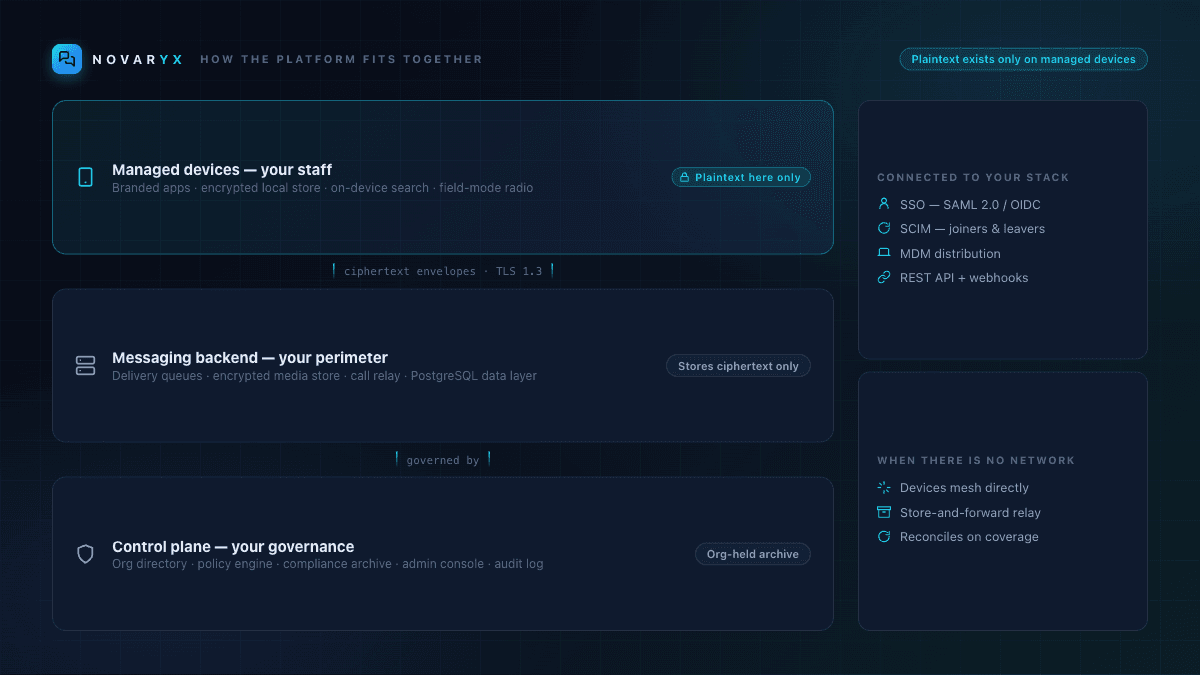
NOVARYX Architecture — Sovereign by Design
Three tiers, one principle: message content exists in plaintext only on managed end-user devices. The backend — deployable on your servers, on a Zeour appliance, or on Zeour-cloud — relays and stores ciphertext, while the control plane gives your organisation the governance consumer apps cannot: directory, policy, archive, and audit. Standards end to end: AES-256-GCM, MLS-aligned group encryption (RFC 9420), TLS 1.3 transport, SAML 2.0 / OIDC / SCIM identity, WebRTC calling.
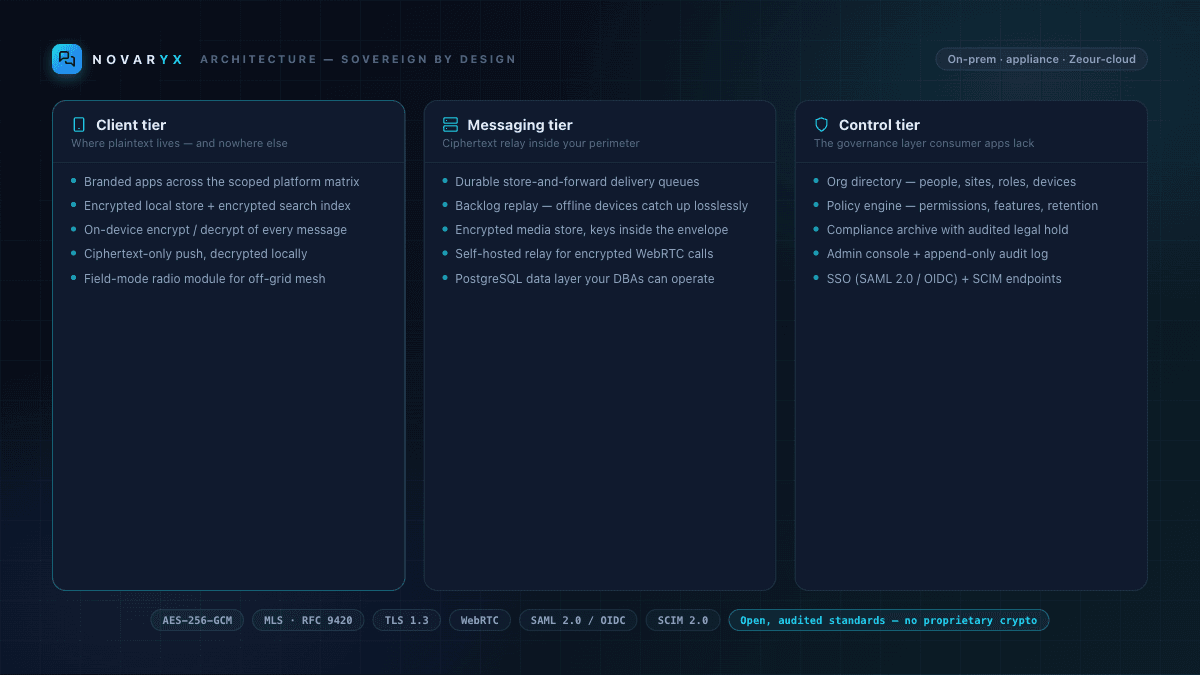
Client Tier — Managed Devices
Where plaintext lives, and nowhere else
- Branded apps across the scoped platform matrix (mobile, tablet, desktop, web)
- Encrypted local message store and on-device encrypted search index
- On-device encryption and decryption of every message and media item
- Private notifications — ciphertext payloads decrypted locally
- Field-mode radio module for off-grid mesh relay
- Distributed and governed through your MDM
Messaging Tier — Your Perimeter
Ciphertext relay and durable delivery
- Delivery service with durable store-and-forward queues and backlog replay
- Encrypted media store — sealed blobs, keys inside the message envelope
- Consume-after-delivery cleanup so relay storage stays minimal
- Self-hosted call relay for encrypted WebRTC voice and video
- PostgreSQL-based data layer your DBA team can operate and back up
- Deployable on your servers, a Zeour appliance, or Zeour-cloud
Control Tier — Governance
The organisational layer consumer apps lack
- Org directory service — people, departments, sites, roles, devices
- Policy engine for messaging permissions, features, and retention
- Compliance archive with legal hold and audited supervisory access
- Admin console with append-only audit log
- SSO (SAML 2.0 / OIDC) and SCIM provisioning endpoints
- REST API + webhooks for enterprise integration
Delivery & Synchronisation
Real-time- Realtime delivery over TLS 1.3 with authenticated channels
- Backlog replay on every reconnect — offline devices catch up losslessly
- Offline outbox — messages queued locally auto-send when connectivity returns
- Off-grid mesh: multi-hop store-and-forward with hop budgets and deduplication
- Cross-mode reconciliation — field-mode traffic syncs to the platform when back in coverage
- Delivery and read receipts advance end-to-end, policy permitting
NOVARYX vs the Alternatives Buyers Actually Consider
Three realistic options for official internal communications — a consumer app your staff already use, a generic cloud chat SaaS, or a platform engineered to your organisation. The right choice depends on how regulated, how sovereignty-sensitive, and how field-operational your organisation is.
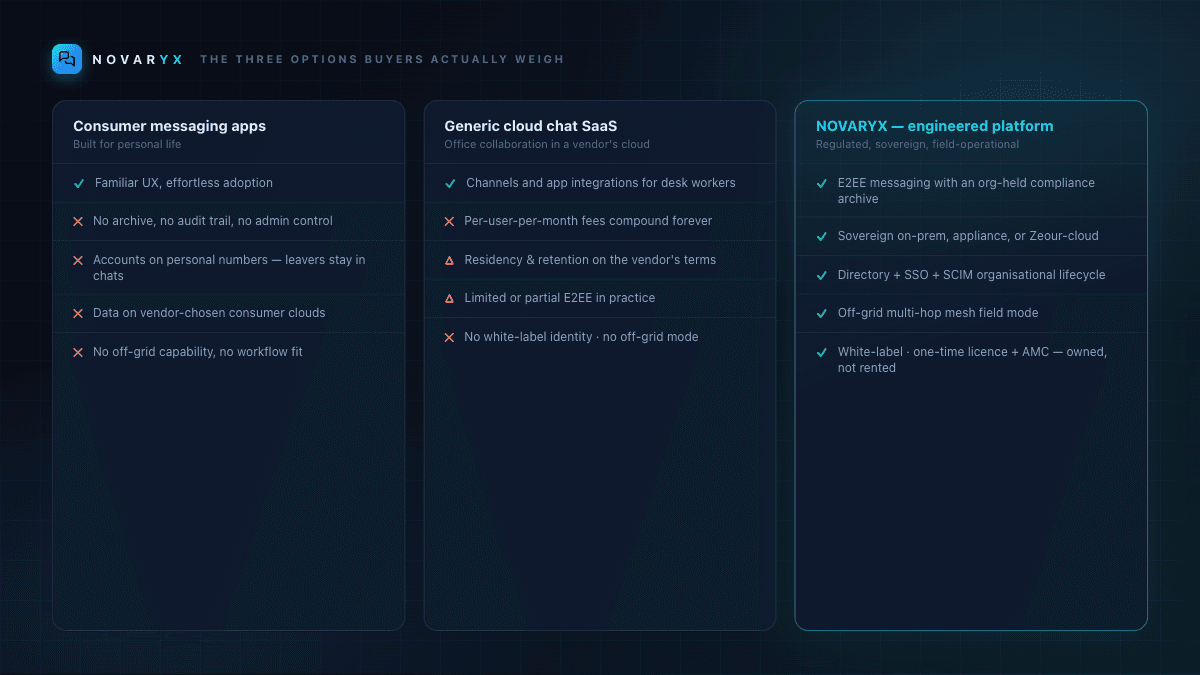
Consumer messaging apps
Best for: Personal life — not official business
- Familiar UX and effortless adoption
- End-to-end encryption for personal chats
- No organisational archive, policy, or admin control
- Accounts bound to personal identities and devices
- Data and backups on vendor-chosen consumer clouds
- No off-grid capability; no workflow fit; no accountability
Generic cloud chat SaaS
Best for: Office collaboration inside one vendor's cloud
- Channels, threads, and app integrations for desk workers
- Per-user-per-month subscription that compounds forever
- Vendor-hosted: residency and retention on the vendor's terms
- Limited or partial end-to-end encryption in practice
- No white-label identity; no off-grid mode
- Field and frontline staff typically left out of licensing
NOVARYX engineered platform
Best for: Regulated, sovereignty-sensitive, and field-operational organisations
- End-to-end encrypted messaging with an org-held compliance archive
- Sovereign on-premises, appliance, or Zeour-cloud deployment
- White-label identity and per-engagement feature scope
- Directory + SSO + SCIM organisational lifecycle
- Off-grid multi-hop mesh field mode
- One-time licence + AMC — owned, not rented
NOVARYX Deployment Checklist
The phased path from first scoping call to an operated, governed communications platform — every phase fixed-fee, every milestone demonstrable.
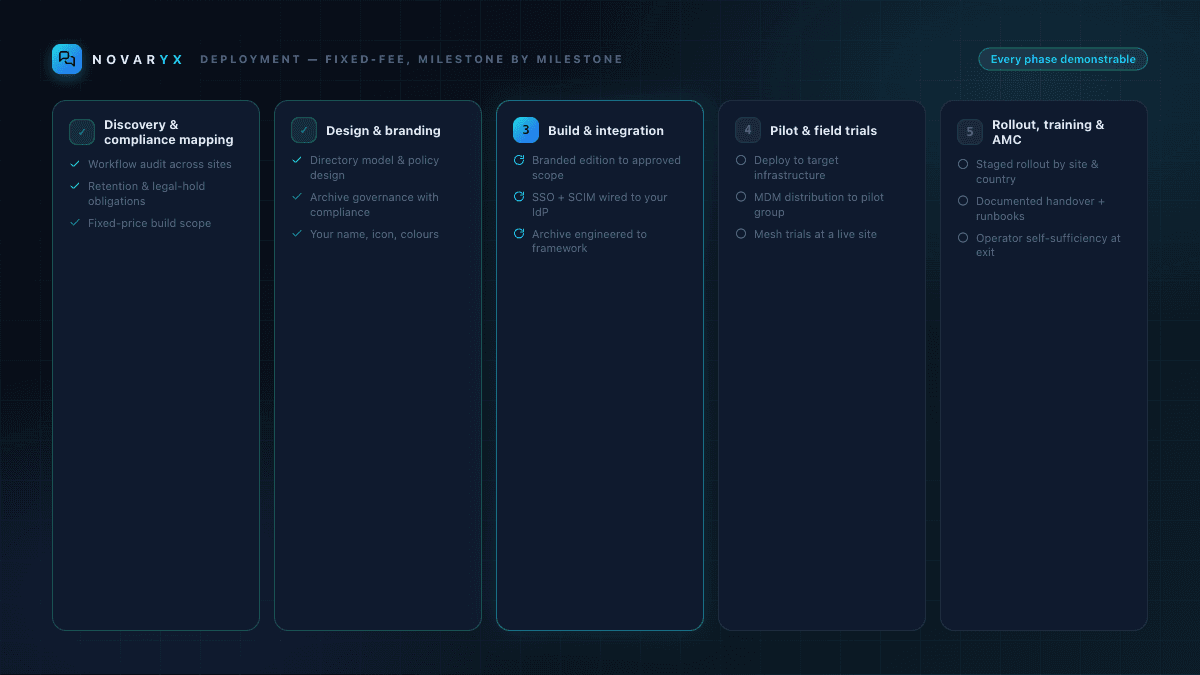
- 01
Phase 1 — Discovery & Compliance Mapping
ChecklistCommunication workflow audit across departments and sitesRegulatory mapping: retention, supervision, legal hold obligationsPlatform matrix and device estate reviewDeployment model decision: on-premises, appliance, or Zeour-cloudIntegration inventory (IdP, HR, ERP, CRM, ITSM, SIEM)Fixed-price build scope with milestone plan - 02
Phase 2 — Design & Branding
ChecklistOrg-directory model and messaging policy designRetention schedules and archive governance with compliance teamAdmin role model and audit requirementsWhite-label identity: name, icon, colours, store/MDM listingLocale set and RTL requirements confirmed - 03
Phase 3 — Build & Integration
ChecklistBranded edition built to the approved scopeSSO (SAML 2.0 / OIDC) and SCIM provisioning wired to your IdPCompliance archive engineered to the mapped frameworkREST / webhook integrations delivered per inventorySecurity review against your organisation's policies - 04
Phase 4 — Pilot & Field Trials
ChecklistBackend deployed to target infrastructureMDM distribution to the pilot device groupPilot cohort runs real traffic with support monitoringOff-grid mesh trials at a representative site (where scoped)Policy and UX adjustments from pilot feedback - 05
Phase 5 — Rollout, Training & Operations
ChecklistStaged rollout by department, site, and countryAdmin, compliance, and end-user training deliveredDocumented handover — runbooks, architecture, restore drillsAMC in force: updates, security patches, operational supportOperator self-sufficiency confirmed as the exit posture
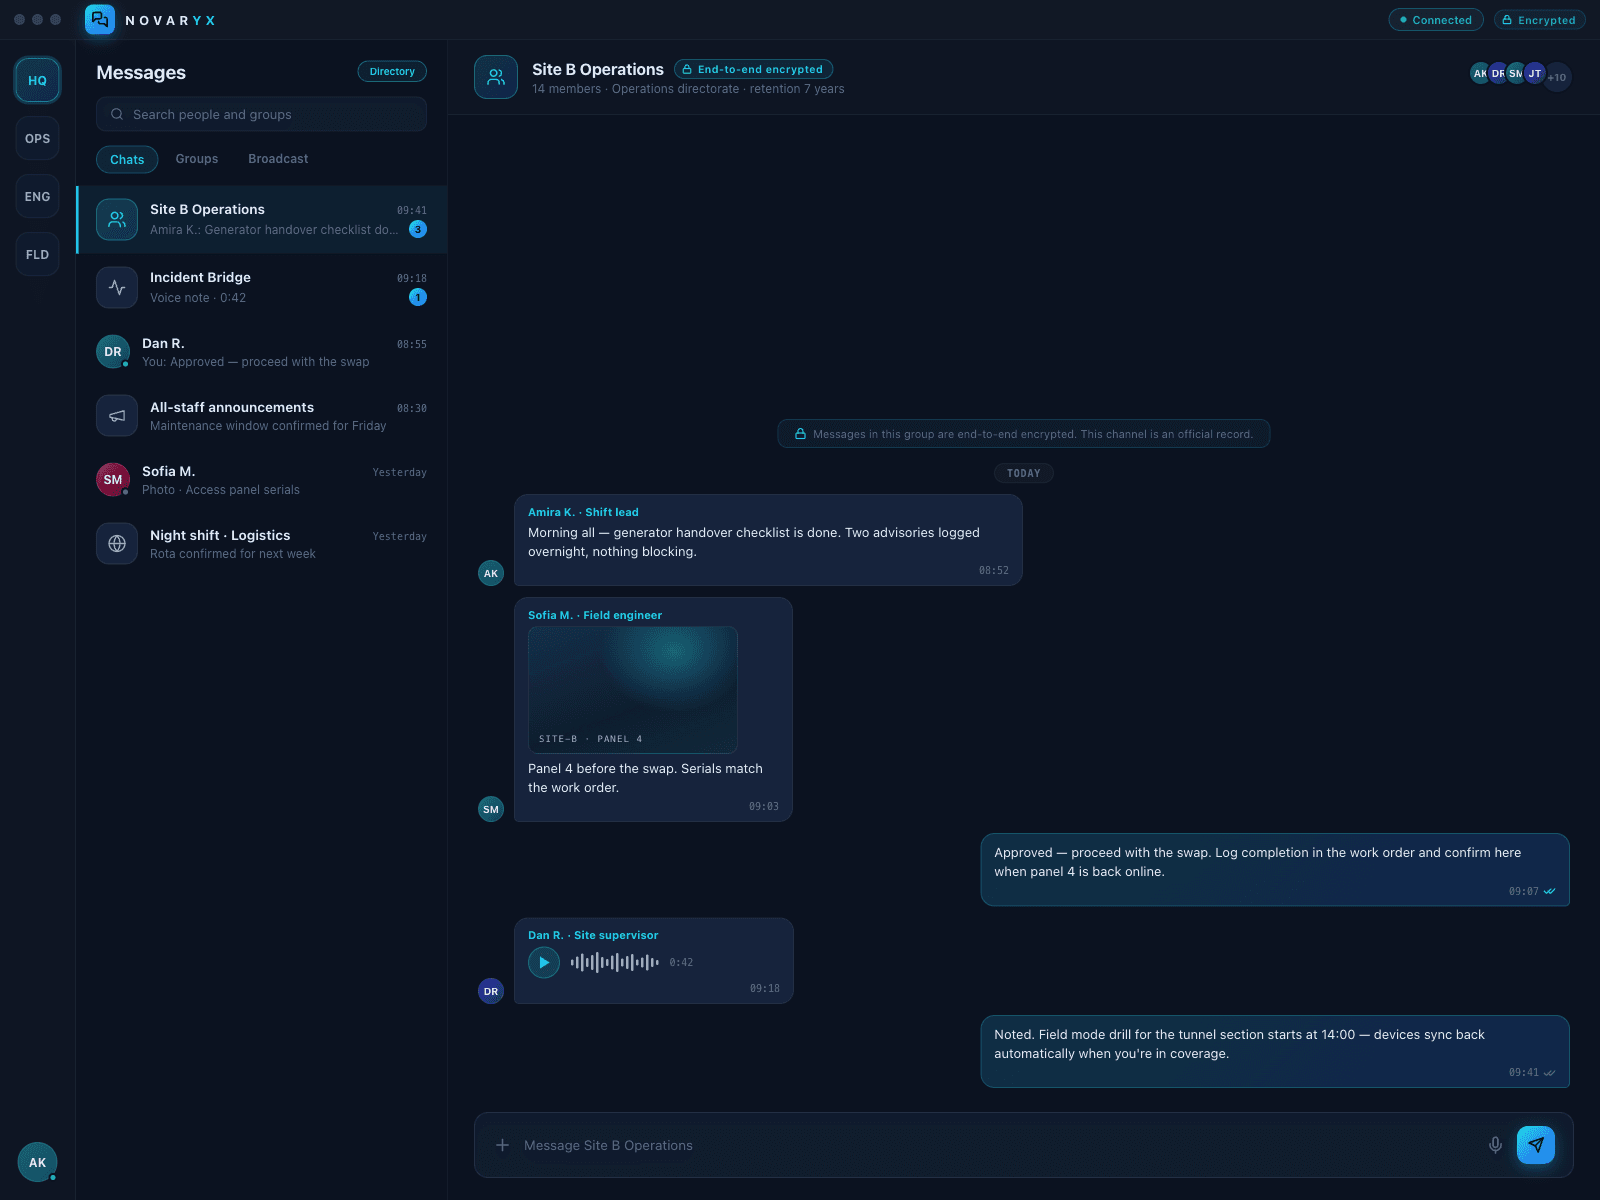
Inside a NOVARYX Deployment
The surfaces of an engineered edition — messaging, governance, field mode, and compliance.
Why Consumer Messaging Apps Fail Official Communications
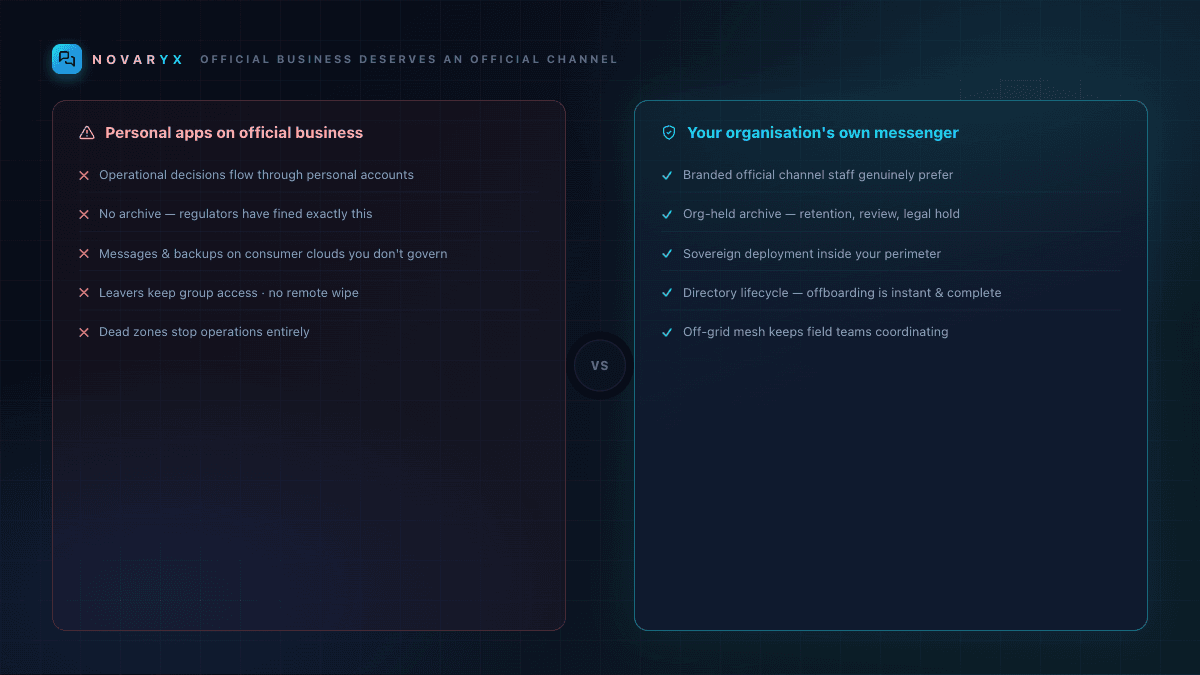
Staff will always use the best channel available. If the best channel is a personal consumer app, official business ends up ungoverned, unarchived, and outside your perimeter.
Official business on personal apps
Operational decisions, customer data, and incident coordination flow through personal accounts on consumer apps — outside organisational control, invisible to compliance, and gone when the employee leaves.
A branded official channel
Your organisation's own messenger — familiar consumer-grade UX under your name, governed by your directory and policy, adopted because it is genuinely the best channel available to staff.
No archive, no audit trail
Regulators in banking and government expect official communications to be retained and reviewable. Consumer apps offer neither — and firms worldwide have paid substantial fines for exactly this gap.
An org-held compliant archive
Retention, supervisory review, and legal hold engineered to your regulatory framework, inside your perimeter, with archive access itself audited.
Data on consumer clouds you don't govern
Message content, metadata, and backups live on infrastructure chosen by the app vendor, in jurisdictions chosen by the vendor — the opposite of data residency and sovereignty policy.
Sovereign deployment
The full backend on your infrastructure — on-premises by default, with an appliance option on Zeour server hardware — or Zeour-cloud where managed operations are preferred.
No organisational lifecycle
Leavers keep group memberships. Accounts bind to personal phone numbers. There is no provisioning, no policy, no remote wipe, no admin console — because those were never the product's job.
Directory-driven lifecycle
SSO + SCIM tie messaging to HR reality: joiners provisioned automatically, leavers deprovisioned instantly, devices wiped remotely, every admin action logged.
Dead zones stop operations
Consumer messengers assume the internet. Remote sites, offshore platforms, basements, tunnels, and disaster scenarios have none — and operations there go silent or fall back to unlogged radio.
Off-grid field mode
Encrypted multi-hop mesh messaging keeps teams coordinating with zero infrastructure, then reconciles with the platform when connectivity returns.
One-size features, zero workflow fit
A generic app cannot express your org structure, your approval flows, your terminology, or your regulator's retention schedule. Workarounds accumulate; governance erodes.
Engineered per engagement
Your workflows, platforms, locales, and compliance obligations are mapped in discovery and built into your edition — the platform fits the organisation, never the reverse.
NOVARYX Messenger Features
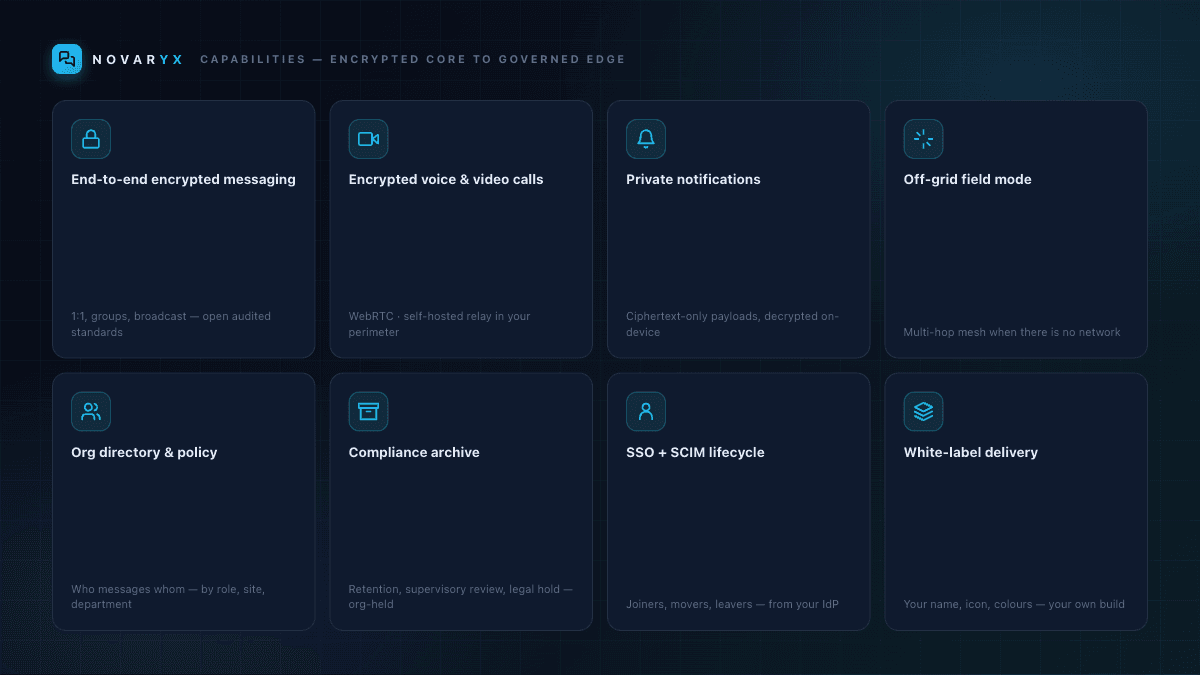
End-to-End Encrypted 1:1 & Group Messaging (Open, Audited Cryptographic Standards)
Encrypted Media Sharing — Images, Documents, Voice Notes
Encrypted Voice & Video Calls (Standards-Based WebRTC)
Disappearing Messages + View-Once Media (Policy-Controlled)
Encrypted On-Device Storage + Encrypted Message Search
Private Push Notifications — Ciphertext-Only Payloads, Decrypted On-Device
Off-Grid Field Mode — Multi-Hop Mesh Messaging with No Network Coverage
Store-and-Forward Delivery with Offline Outbox & Auto-Resend
Org Directory Access Model — Messaging Policy by Department, Role & Site
Compliant Message Archiving — Retention, Audit & Legal Hold to Your Regulator's Requirements
Admin Console — Users, Devices, Policy, Remote Wipe, Usage Reporting
Enterprise Identity — SAML 2.0 / OIDC Single Sign-On + SCIM Provisioning
Broadcast Channels & Announcement Groups with Read Tracking
Message Controls — Edit, Delete-for-Everyone, Reply, Star, Forward Limits
Read Receipts, Presence & Typing Indicators (Policy-Configurable)
Key Transparency — Identity-Key Pinning with Security-Change Alerts
White-Label Branding — Your Name, Your Icon, Your Colours, Your Store Listing
Sovereign On-Premises Deployment or Zeour-Cloud Hosting
On-Premises Appliance Option on Zeour Branch-Class Server Hardware
Multi-Platform per Engagement — Mobile, Tablet, Desktop, Web
Engineered Multilingual — Full RTL Baseline, Any Locale per Engagement
Role-Based Administration + Append-Only Audit Log
REST API + Webhooks — ERP / CRM / HR / ITSM Integration Surface
MDM-Managed Distribution to Corporate Device Fleets
One-Time Licence + Annual Maintenance Contract (AMC) Commercial Model
NOVARYX Messenger Components
Encrypted Messaging, Directory Controls and Archive Governance.
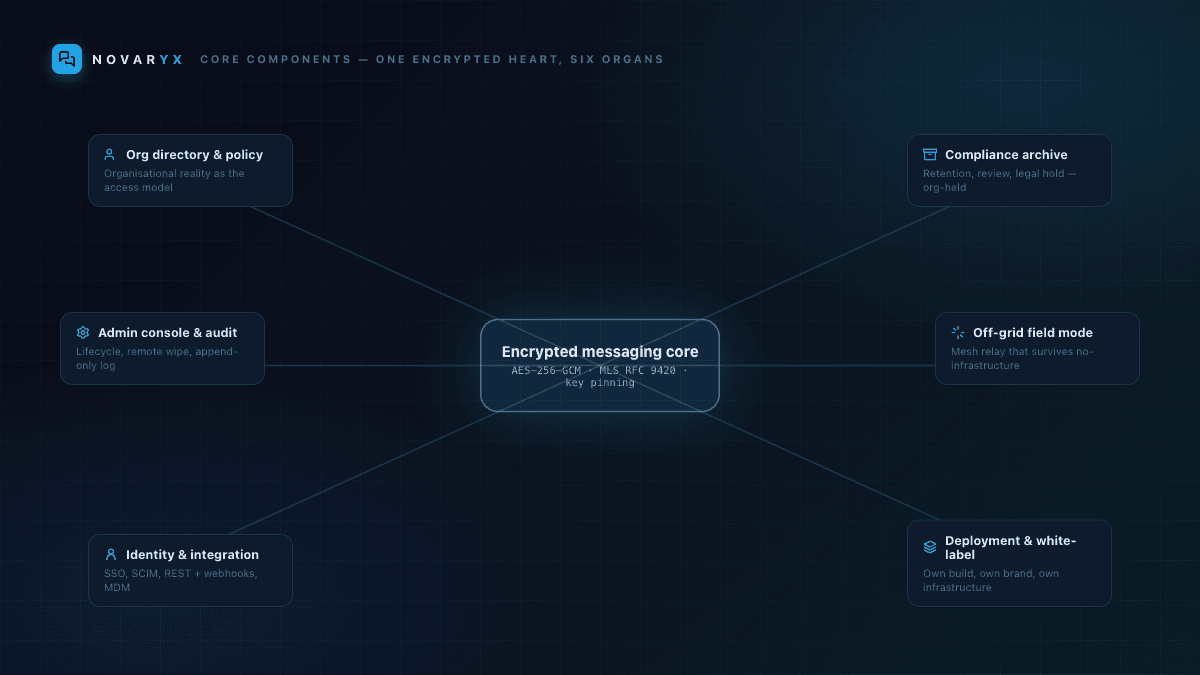
Admin Console & Audit
The operational surface for IT, security, and compliance teams.
- User and device lifecycle management
- Remote wipe of the app container
- Usage and adoption reporting
- Broadcast and announcement administration
- Append-only audit log of admin actions
Identity & Integration Layer
Your identity stack as the front door; your business systems as first-class citizens.
- SAML 2.0 / OIDC single sign-on
- SCIM joiner-mover-leaver provisioning
- REST API and webhook surface
- ERP / CRM / ITSM / SIEM integration patterns
- MDM-managed distribution
Deployment & White-Label Layer
Every customer edition is its own build against its own infrastructure.
- Sovereign on-premises or Zeour-cloud topology
- Appliance option on Zeour branch-class servers
- Full brand identity — name, icon, colours, listing
- Platform matrix scoped per engagement
- Documented handover and operator self-sufficiency
Communication Governance and Operational Continuity
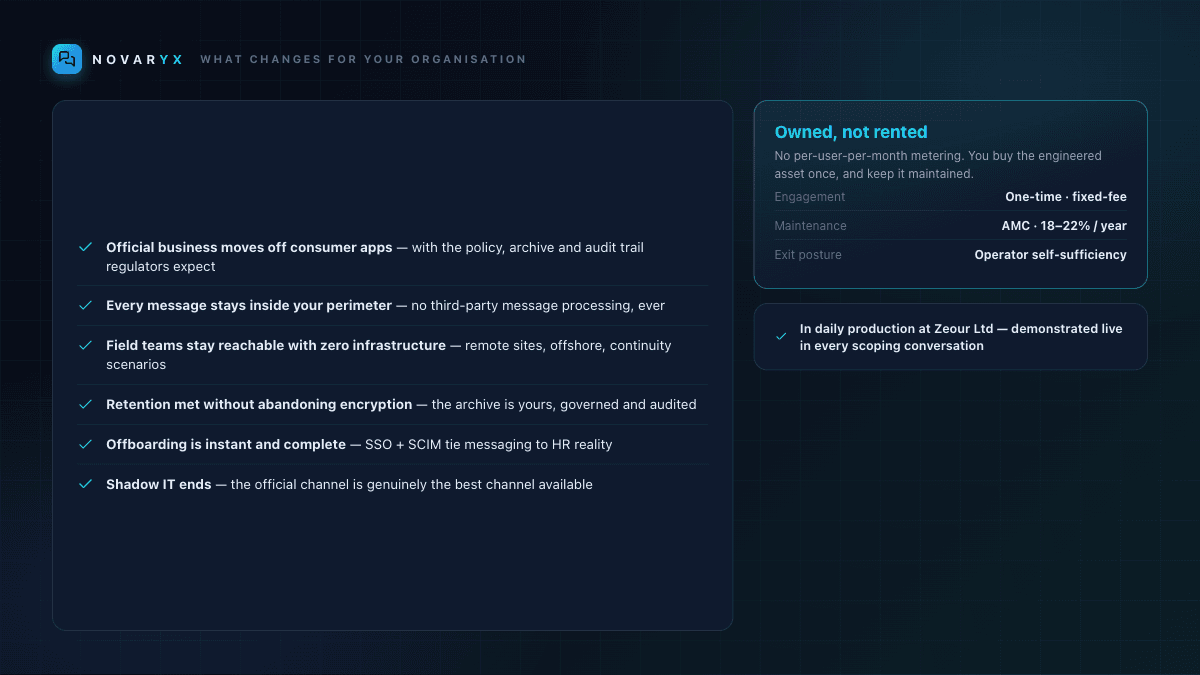
Move official business off consumer chat apps — with the policy, archive, and audit trail regulators expect
Keep every message inside your perimeter — sovereign on-premises deployment with no third-party message processing
Stay reachable when the network is not — off-grid mesh field mode for remote sites, offshore operations, and continuity plans
Meet records-retention obligations without abandoning encryption — an archive engineered to your regulatory framework, held by your organisation
One branded app your staff actually adopt — consumer-grade UX under your name and your rules
Eliminate shadow IT by making the official channel better than the unofficial one
Own the deployment — one-time licence, documented configuration, operator self-sufficiency at exit
Provision and deprovision from your identity stack — joiners and leavers handled by SSO + SCIM, not chat invites
Scale one policy model from a single office to a multi-country estate
Proven in daily production at Zeour Ltd — we run our own official communications on it
From Messaging Requirements to Organisational Rollout
Define communication policy, configure the edition and validate it with the teams who will use it.
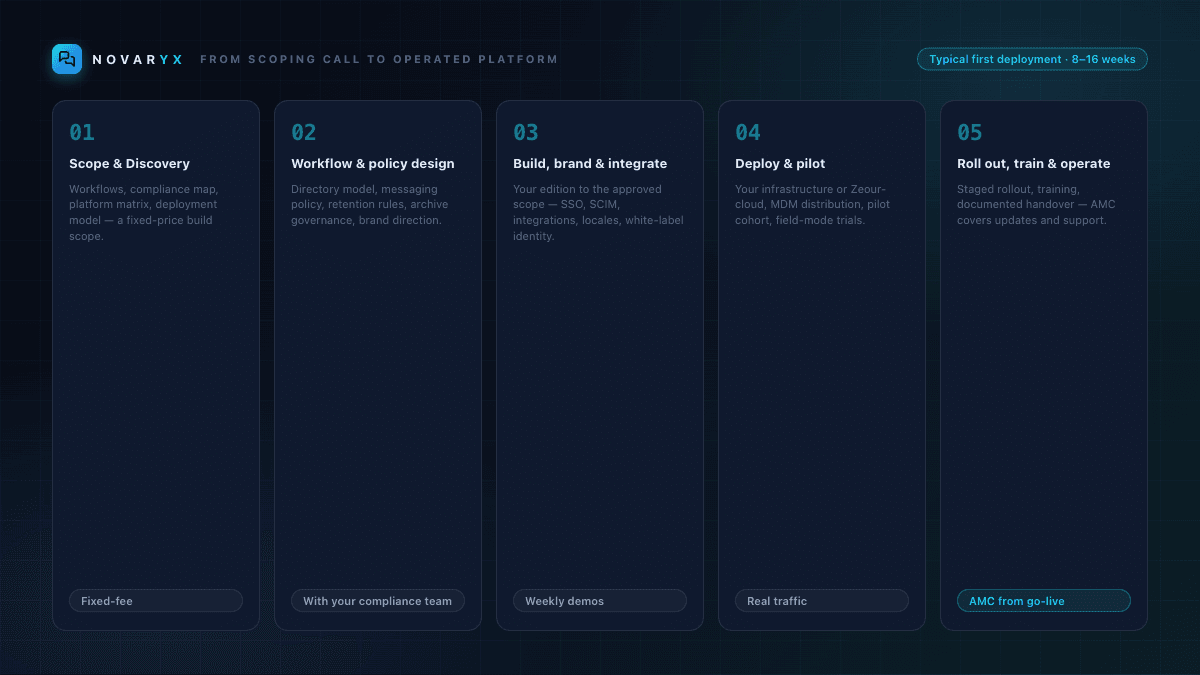
Scope & Discovery (Fixed-Fee)
We map your communication workflows, compliance obligations (which regulator, what retention, who audits), platform matrix, device estate, integration list, and deployment model — sovereign on-premises or Zeour-cloud. Output: a fixed-price build scope with a milestone plan.
Workflow & Policy Design
Org-directory model (who can message whom), messaging policy (receipts, disappearing windows, forwarding limits), retention and legal-hold rules, admin roles, archive access governance, and your white-label brand direction — designed with your compliance and IT teams before anything is built.
Build, Brand & Integrate
Your edition is built to the approved scope: name, icon, colours, feature set, locales. Identity is wired to your SSO (SAML 2.0 / OIDC) with SCIM provisioning; REST + webhook integrations connect HR, ERP, CRM, or ITSM systems where scoped.
Deploy & Pilot
Deployment lands on your infrastructure (or Zeour-cloud), distributed to managed devices through your MDM. A pilot group runs real traffic; where field mode is in scope, off-grid mesh trials run at a representative site before rollout.
Roll Out, Train & Operate
Staged rollout across departments and sites, admin and end-user training, and a documented handover. The Annual Maintenance Contract covers updates, security patches, and operational support — with operator self-sufficiency as the exit posture.
NOVARYX Messenger Use Cases by Industry
Explore the service environments relevant to novaryx messenger.
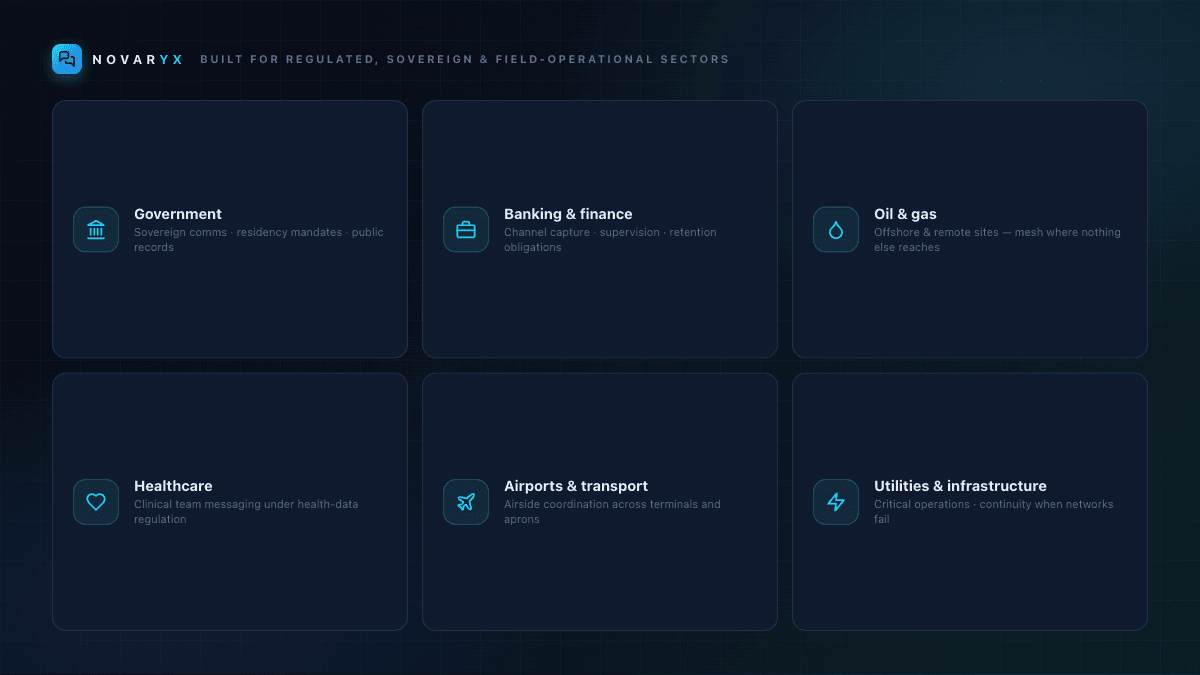
Open the deep dive by vertical
Customers running NOVARYX Messenger in production
1 featured deployment where NOVARYX Messenger ships today — a selection from a much wider production portfolio. Click any card for the full case-study deep dive.
Secure Enterprise Messaging Platform FAQs
Get answers to the most common questions about our novaryx messenger.
What is NOVARYX Secure Messaging Platform?
Is NOVARYX only for large enterprises and government?
Is NOVARYX available off the shelf?
How does the end-to-end encryption work?
Can we archive messages for compliance and legal hold?
What is off-grid field mode?
Which platforms are supported?
Is NOVARYX deployed on-premises or in the cloud?
How does white-labelling work?
How do users sign in — do we manage another user database?
What does NOVARYX integrate with?
How is this different from the consumer messaging apps our staff already use?
Who can read our messages?
How long does a NOVARYX deployment take?
How does NOVARYX pricing work?
Is Zeour actually using NOVARYX itself?
Can NOVARYX run on Zeour hardware?
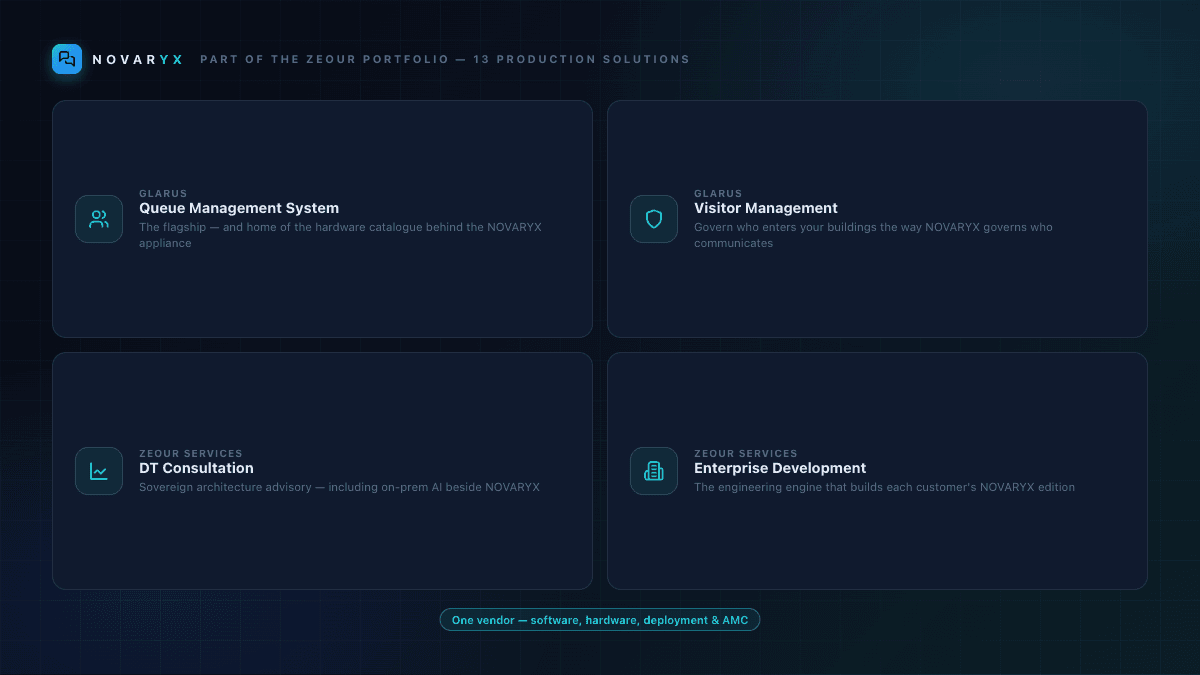
Explore Related Solutions
Review the engineering, advisory and facility-management services relevant to organisational governance.
Ready to Transform Your Operations with NOVARYX Messenger?
Discuss your workflows, deployment requirements and integration scope with the Zeour team.
NOVARYX Messenger — concepts you'll meet
Definitions for the operational terms that appear across this page. Tap any chip to read the long-form entry plus its cross-links.